Phishing App 'SKR Claim' Featured in Solana dApp Store for One Hour
Written with artificial intelligence.
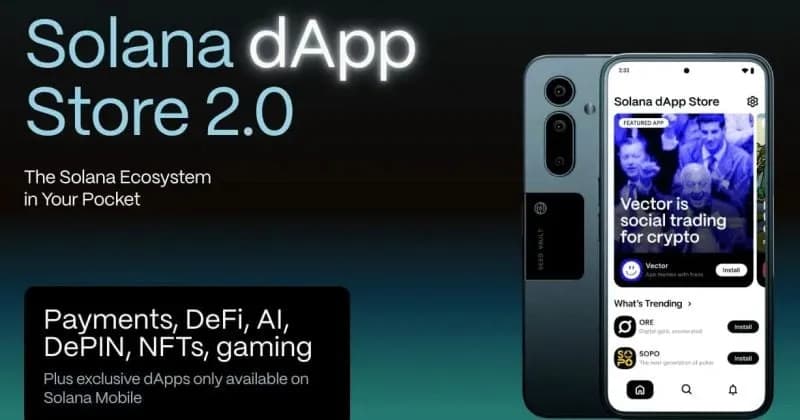
A phishing application named 'SKR Claim' appeared in the Solana dApp Store's Spotlight for one hour on November 1 after unauthorized access to the dApp Publishing Portal. The app prompted users for their seed phrases, leading Solana Mobile to remove it and address the security vulnerability.
Unauthorized Access to dApp Publishing Portal
On November 1, Solana Mobile reported that a phishing app called 'SKR Claim' was submitted to its dApp Store after unauthorized access to the dApp Publishing Portal. This app was live in the store's Spotlight for an hour before being taken down. Solana Mobile confirmed that the app requested users to input their private seed phrases, raising significant security concerns.
Security Measures and Response
The attackers not only submitted the phishing app but also modified the App Spotlight and Quests interfaces, which are designed to showcase applications and tasks. Solana Mobile has since fixed the vulnerability that allowed this unauthorized submission, although details on how the intruder accessed the portal remain unclear. Importantly, the Seed Vault, which securely stores wallet keys, was not breached, as it requires user approval for any transactions.
User Precautions
Solana Mobile is currently in the process of removing 'SKR Claim' from all devices that installed it, but it has not confirmed whether this removal has been fully completed. Users who entered their seed phrases into the app should consider their wallets compromised and should create new wallets with fresh recovery phrases. They are advised to transfer any remaining assets immediately.
Official Guidance
Solana Mobile emphasizes that their team will never ask users for their seed phrases or for cryptocurrency. Furthermore, they will not request wallet connections to external apps or sites for airdrop claims. The 'SKR Claim' app exploited the name of the native token of the Solana Mobile ecosystem, which may have contributed to its temporary visibility in the store's Spotlight.